Understanding Cyber Defence Strategies For Modern Software Development
Software development involves more than creating functional applications and writing efficient code. It also requires careful planning to protect applications from security threats, unauthorised access, and potential data exposure. Cyber defence helps developers recognise vulnerabilities, strengthen application security, and maintain dependable software systems. By understanding practical defence strategies, development teams can address security concerns early, protect essential resources, and build applications that remain resilient as technologies and technical requirements evolve.
1. Recognising Emerging Cybersecurity Threats
Modern applications face cybersecurity threats that can affect functionality, expose information, and disrupt operations. Common risks include malicious software, phishing attacks, injection vulnerabilities, and unauthorised access attempts. Outdated libraries and poorly configured systems can also create weaknesses that attackers may exploit. Understanding these threats helps developers identify potential entry points, evaluate risks, and recognise how minor coding mistakes can create larger security problems.
Developers should examine how information enters applications, how permissions are assigned, and how external components interact with existing systems. Reviewing previous incidents and following security advisories helps teams understand changing attack methods. Rather than assuming applications remain protected after development, teams should continuously evaluate potential threats and adjust defensive strategies according to application architecture, functionality, and intended usage.
2. Building Stronger Application Defences
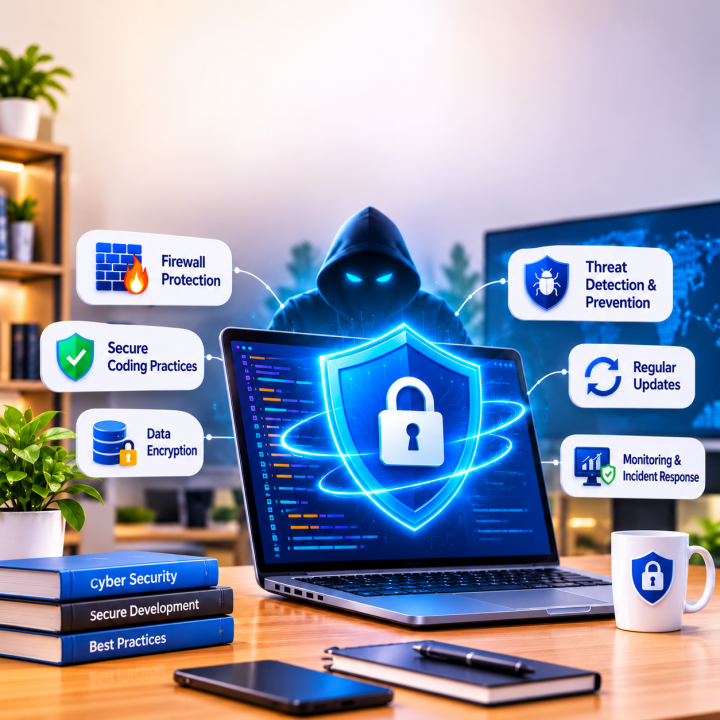
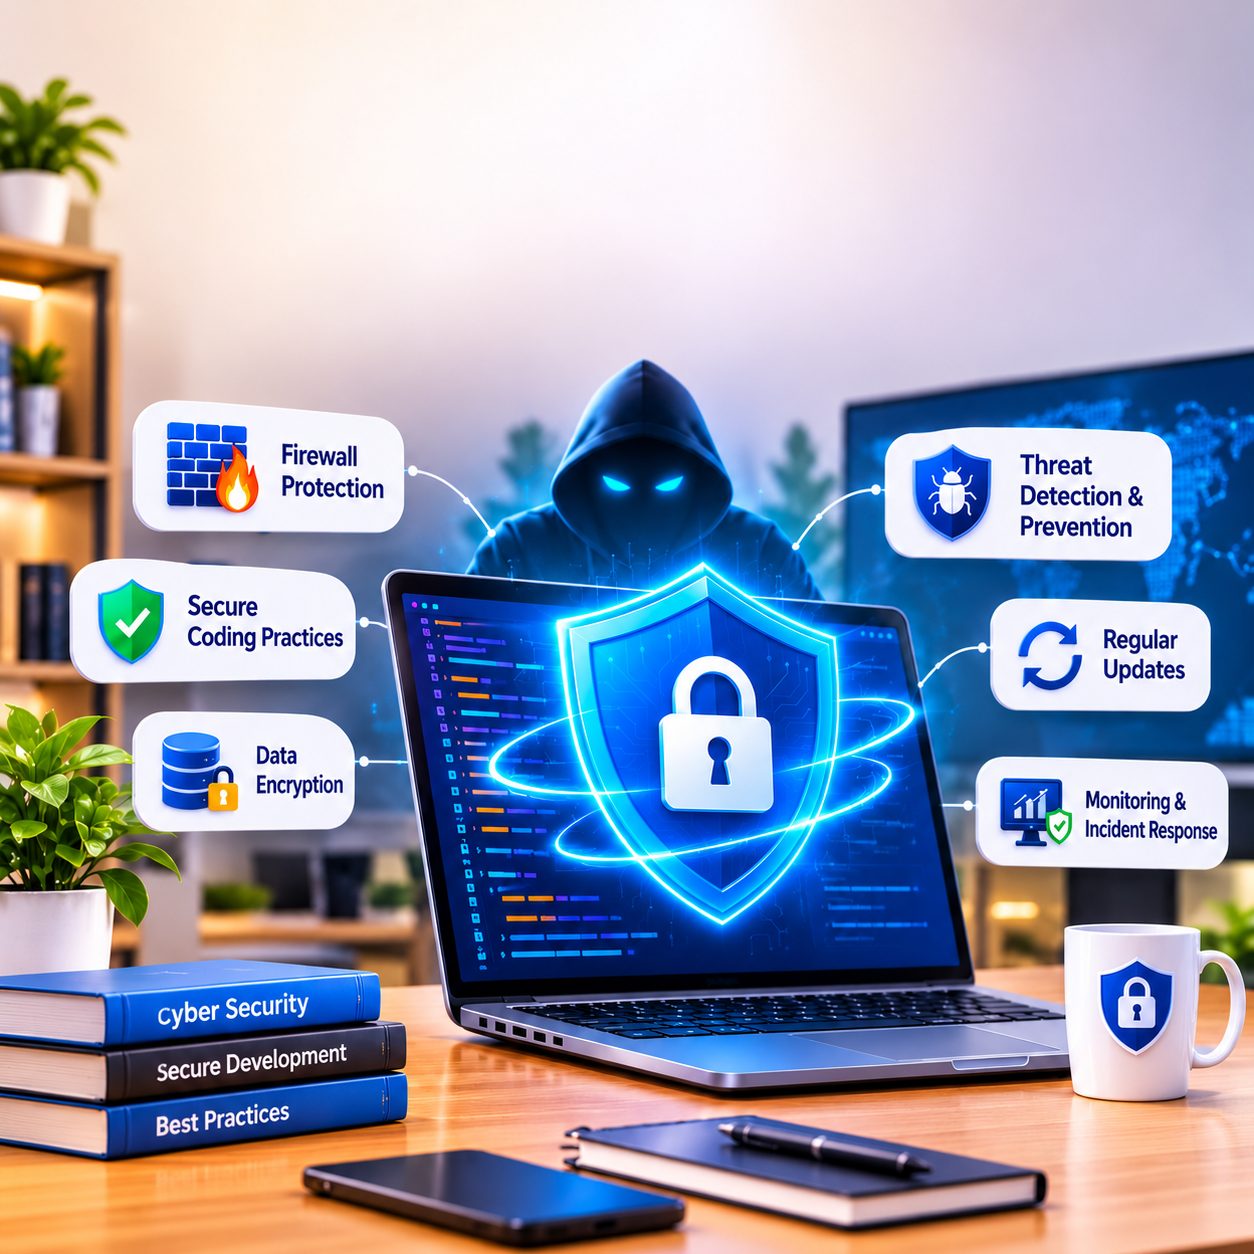
Secure coding provides an essential foundation for protecting software against common vulnerabilities. Developers can validate user inputs, use parameterised database queries, and apply appropriate authentication methods to reduce security risks. Restricting permissions ensures that users access only necessary resources. Sensitive information, including passwords and secret keys, should never be unnecessarily exposed within source code. These measures help prevent common weaknesses while supporting responsible software development practices.
Application security also depends on dependable frameworks, correct system configurations, and careful management of third-party dependencies. Developers should remove unnecessary components, replace outdated packages, and review configuration settings before deployment. Encrypting sensitive information where appropriate helps protect data during storage and transmission. Clear coding standards and regular peer reviews encourage consistent security practices, helping developers reduce vulnerabilities and build stronger foundations for reliable application performance.
3. Detecting Vulnerabilities Through Testing
Security testing helps development teams discover weaknesses that ordinary software checks might overlook. Static code analysis identifies suspicious coding patterns, while dependency scanning highlights known vulnerabilities within external libraries. Penetration testing examines application responses to simulated attacks, revealing weaknesses in defensive mechanisms. Combining suitable testing approaches allows developers to investigate problems, prioritise important findings, and address vulnerabilities before they create significant operational difficulties.
Testing should continue throughout development rather than occurring only before an application launches. Automated security checks can become part of development pipelines, helping teams identify problems whenever code changes. Manual reviews remain valuable when investigating complex logic, authentication processes, and unusual application behaviour. After correcting vulnerabilities, developers should repeat relevant tests to confirm their changes work correctly. Maintaining testing records also helps teams recognise recurring issues and improve future security practices.
4. Maintaining Protection After Deployment
Releasing an application does not end cybersecurity responsibilities. New vulnerabilities can emerge in operating systems, development frameworks, external libraries, and supporting infrastructure. Developers should monitor security advisories, apply appropriate updates, and remove unnecessary components. Reviewing access permissions periodically helps prevent excessive privileges. These maintenance activities reduce exposure to known weaknesses and help applications remain functional, compatible, and prepared for changing security requirements.
Continuous monitoring provides another important layer of cyber defence after deployment. Application logs can reveal unusual login attempts, unexpected system behaviour, or activities requiring investigation. Teams should establish clear procedures for reporting incidents, assessing their impact, and implementing corrective measures. Documenting lessons from security issues helps developers strengthen future projects. By combining regular maintenance, monitoring, and effective communication, organisations can protect software and maintain stronger security practices throughout an application's lifecycle.